Skip to content
Contract-aware revenue integrity for hospitals and health systemsEvery finding cites the contractReport-only, your team decidesHIPAA BAA signed before any data moves

HomeSecurity

Security and compliance

Report-only, under a signed BAA

Clinical Speed works under a signed HIPAA Business Associate Agreement, with patient details masked by default, and never changes a claim, a code or a posted transaction.

BAA signed before any file movesPatient details masked by defaultReport-only, nothing written back

Governance

Report-only by design

The engine reports and the hospital decides, and that division is built into the platform for every hospital and every user.

Clinical Speed works the analysis and the recovery cases, while the hospital's own staff remain the only people who change a claim, a code or a charge, under the guardrails below in every engagement.
  • Findings never write themselves into the 837.
  • Coders and HIM keep every coding decision.
  • Posted transactions are left untouched, and there is no write to the billing ledger.
  • Clinicians decide every question of care, and the Care Gap Review never touches a claim.
  • Chargemaster changes are uniform prices for every payer, adopted by the hospital's own committee.
  • Expected allowed equals the contract, with no revenue-inflation logic.
  • No appeal file moves without the hospital's verification.
  • Data stays in the authorized environment, and no shadow EHR is created.
  • Access the hospital grants is named, read-only EHR and payer-portal accounts for the records an appeal needs, with minimum-necessary scope and multi-factor sign-in where supported.
  • Access is removed when the engagement ends, and any download the hospital approves stays inside the authorized environment.

The evidence packs behind each finding serve as audit workpapers, since each one cites the contract clause, the rate column, the rule and the calculation. Compliance, internal audit and legal can trace any finding from its source document to its dollar amount, and the hospital keeps every pack. A hospital can put a report-only contract engine in front of those reviewers and approve it, which a black-box editor that changes claims cannot offer.

Protected health information

The BAA and patient data in the platform

The Business Associate Agreement

The Business Associate Agreement binds Clinical Speed to use and disclose protected health information only as the services require and only to the minimum necessary, under 45 CFR 164.502(b) and 164.514(d). Safeguards include encryption, access controls, contingency, backup and disaster-recovery plans and security training for every person with access. Any subcontractor that touches protected health information is bound to the same terms. Clinical Speed reports any breach no later than ten business days after discovery, with the content the agreement lists, and supports patient requests for access, amendment and an accounting of disclosures within ten business days. At the end of the engagement, protected health information is returned or destroyed.
Patient data inside the platform

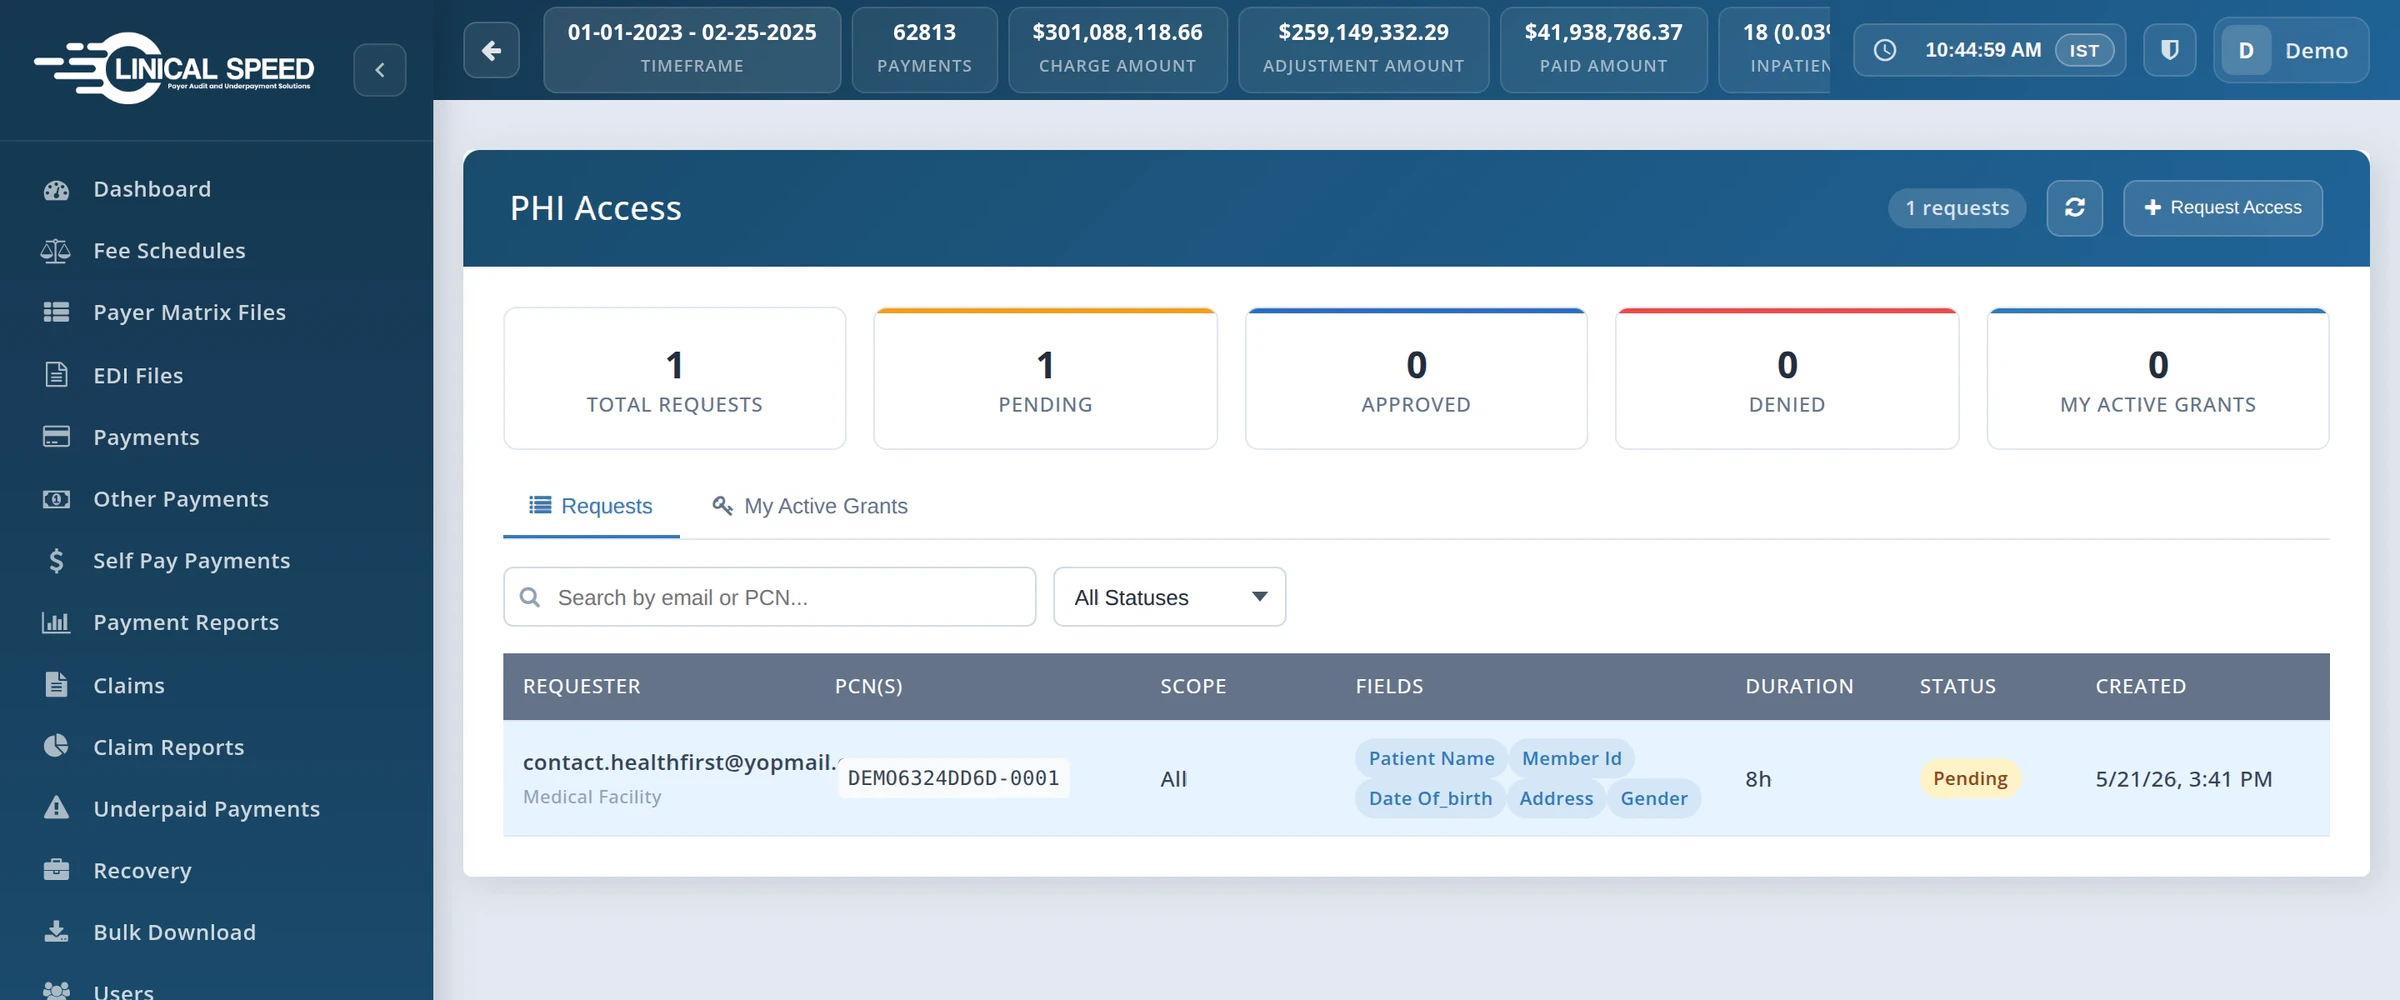
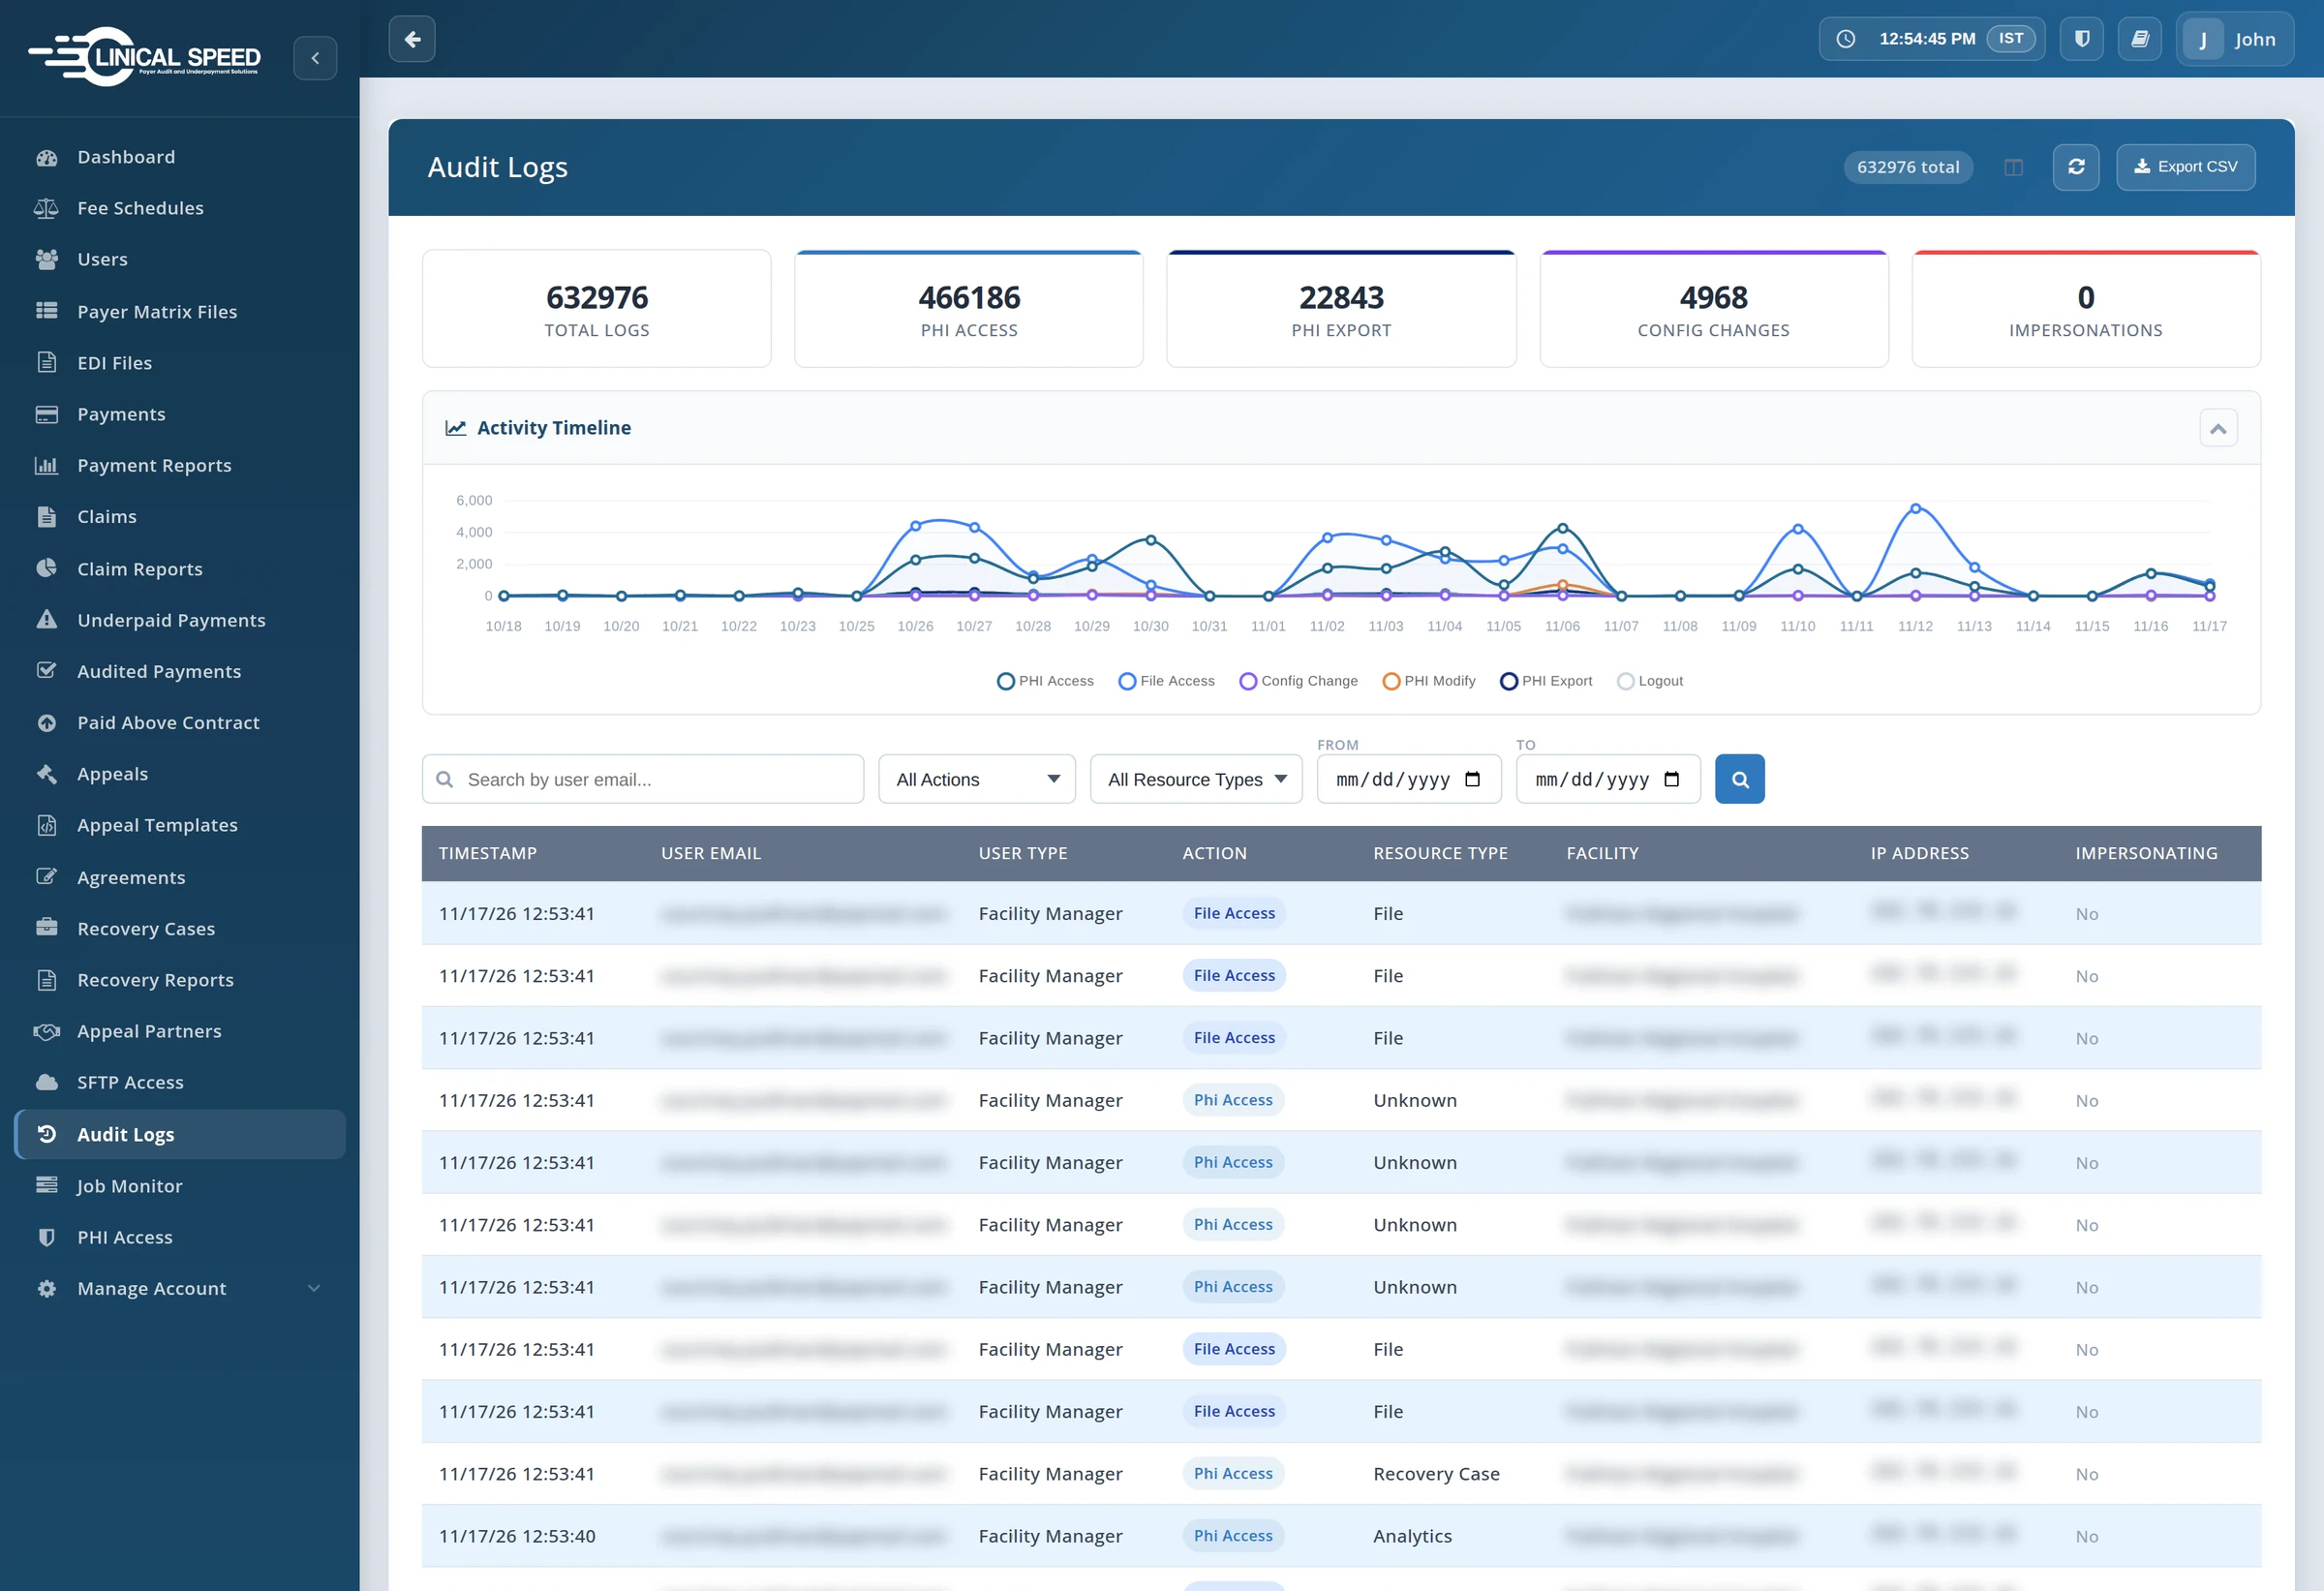
Patient details are masked by default for every user of the platform. A user who needs a patient field requests it per claim and per field, among name, member ID, date of birth, address and gender, with a written reason of at least 50 characters and a duration of 8, 24 or 48 hours. Each request is approved or denied by an administrator, and the access expires on its own at the end of the period. Every view and export of protected health information and every configuration change is recorded in audit logs with the user and IP address, and the logs export to CSV for the hospital's own review.

The PHI access screen: a request for named patient fields on one claim, for eight hours, pending an administrator's approval
PHI Access · patient fields stay masked until an administrator approves a request
The audit log: every PHI access, PHI export and configuration change recorded with its user, facility and IP address, with user details blurred
Audit Logs · user details blurred for this page

For IT and security review

Hosted on AWS, encrypted at rest and in transit

The platform is hosted on Amazon Web Services with encryption at rest and in transit, separate file-transfer credentials for each hospital and a standard set of AWS services for access, logging and monitoring. These services are listed below for the hospital's IT and security review.
  • TLS on every connection, with HSTS holding browsers to HTTPS, and a second AES-256 encryption layer on sensitive API payloads with keys derived per session.
  • Encryption at rest for the MongoDB Atlas database on AWS and for documents in Amazon S3 under AWS Key Management Service keys, reached only through short-lived links.
  • Sign-in through AWS Cognito with an email one-time code for multi-factor authentication, access tokens that expire within the hour, and no passwords stored by Clinical Speed.
  • Role-based access, with each facility's users locked to their own facility on the server, and account lockout after three failed sign-ins.
  • Audit logging through AWS CloudTrail, with monitoring through CloudWatch, Security Hub, Amazon Macie and AWS Config.
  • AWS WAF, private VPC networking and AWS Secrets Manager, with temporary credentials and credential rotation.
  • Key-based SFTP through AWS Transfer Family, public-key only, with a separate home directory and keys for each hospital. Rotation retires the old key, and every key generation and rotation is logged.
  • Audit logs retained for six years, in line with HIPAA's six-year documentation retention.

Contract terms

Ownership, insurance and regulation

Data ownership and insurance

The hospital's data and every deliverable belong to the hospital, and Clinical Speed keeps only its own software and methods. Data is exported to the hospital within 60 days after the engagement ends. Confidentiality obligations survive for five years, and longer for protected health information. The hospital may audit Clinical Speed's records for the engagement up to twice in any twelve months. Clinical Speed is insured for professional liability and for cyber and privacy liability, and a certificate is available on request.

Regulatory compliance

The services agreement commits Clinical Speed to the federal Anti-Kickback Statute, the Stark Law, the False Claims Act, the Beneficiary Inducement Statute, the Anti-Solicitation Statute and HIPAA. Every appeal is grounded in the hospital's verified finding and the contract's own terms, which keeps each dispute within what the payer agreed to pay. Expected payment equals the contract with no inflated target, so no appeal asks a payer for more than its agreement allows.

For IT and security review

Security documentation for your review

The Security and Compliance Overview is a vendor self-attestation, our good-faith description of the controls in the production system. It is available to your CIO, privacy officer and compliance team on request.